


The company has worked with more than 300 organisations worldwide and responded to more than 50 cyber incidents
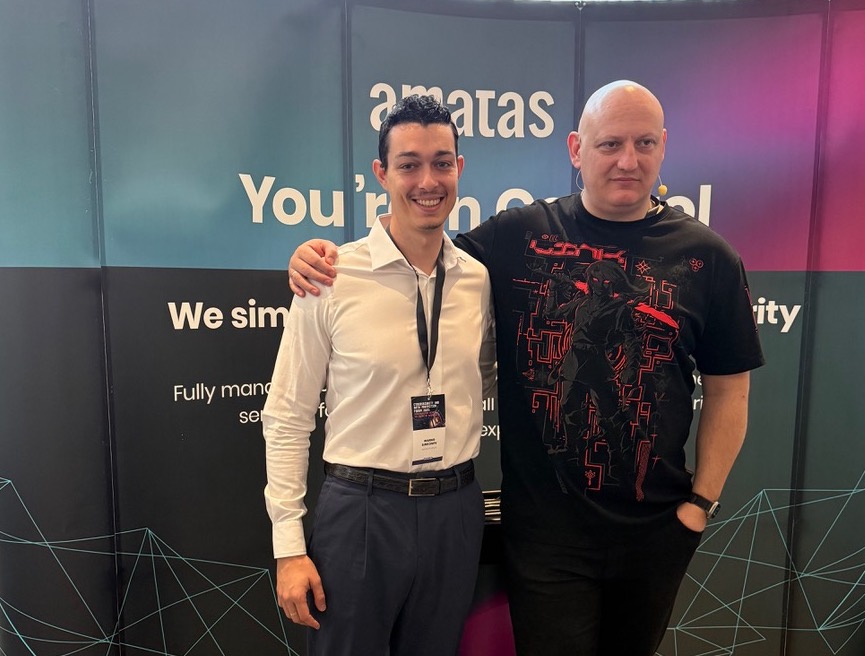
Ten years ago, cybersecurity was still rarely on the agenda of company leadership. It was in this environment that, in 2016, Atanas Simeonov and Boris Goncharov founded AMATAS with the aim of building a Bulgarian company focused entirely on cybersecurity. Today, the company is led by Marko Simeonov, CEO of AMATAS, who has experience in developing and scaling companies in the cybersecurity sector and leads the company's business development and international expansion.
AMATAS marks its 10th anniversary having worked with more than 300 clients in Bulgaria, Europe, North America, Asia and Africa. During this time, its team has responded to more than 50 cyber incidents and carried out security testing for organisations of vastly different sizes, from some of the world's largest companies to hospitals, manufacturing businesses and financial-sector start-ups.
But AMATAS's decade in business also reflects a market that has changed significantly.
Attacks have become more automated, companies' infrastructure more complex, while regulations such as NIS2 and DORA have turned cyber risk into an issue that increasingly requires the attention of both IT teams and management.
"Over the past ten years, we have seen a huge change in the way companies view cybersecurity. Previously, conversations often began with why investment in cybersecurity was necessary. Today, the questions are very different: where is the real risk, are we ready to respond, and how can we use our resources more effectively?" says Marko Simeonov, CEO of AMATAS.
From individual tests to continuous protection
Over the years, AMATAS has expanded its portfolio of services in response to changing threats and organisations' needs. Today, the company provides penetration testing and offensive security, 24/7 monitoring and response through MXDR, virtual CISO services, cyber risk and regulatory compliance management, security awareness and incident response.
Penetration testing remains one of AMATAS's key areas of expertise. The company is CREST-accredited, and in 2026 it expanded its offensive security portfolio to include Purple Teaming, an approach that brings offensive and defensive teams together to help organisations assess whether an attack is possible and whether they can detect and stop it in time.
Alongside developing its services, the company also invests in automating security testing processes. Its practical experience in this field has also led to the creation of Plainsea, a technology company focused on developing agentic AI and autonomous technologies for offensive security.
10 years of change in cybersecurity
According to the AMATAS team, one of the most significant changes over the past decade is that organisations can no longer treat cybersecurity as a series of separate projects.
Cloud services, reliance on external providers, constantly changing infrastructure and the growing use of AI are creating an environment in which risk changes every day. At the same time, European regulations such as NIS2 and DORA are setting increasingly clear requirements for how companies manage and demonstrate their cyber resilience.
This is also changing the role of cybersecurity providers, from carrying out individual technical tasks to becoming long-term partners who need to understand technology, risk and the wider business context.
"There is no point at which an organisation can say that it has finished with cybersecurity. Technology changes, businesses change and attackers adapt. That is why protection must be a continuous process, rather than a task that can simply be marked as completed," Marko Simeonov adds.
After ten years in the market, AMATAS remains focused on developing practical cybersecurity services while adapting them to the new environment, from automation and AI to increasingly demanding requirements for business cyber resilience.
About AMATAS
AMATAS is a Bulgarian cybersecurity company founded in 2016. It provides managed and consultancy cybersecurity services, including penetration testing, MXDR, virtual CISO, security awareness, incident response, red and purple teaming, and support with regulatory compliance.
AMATAS works with organisations across different industries and markets, combining specialist expertise, technology and continuous monitoring to manage cyber risk.
-
COMMENTING RULES
Commenting on www.vagabond.bg
Vagabond Media Ltd requires you to submit a valid email to comment on www.vagabond.bg to secure that you are not a bot or a spammer. Learn more on how the company manages your personal information on our Privacy Policy. By filling the comment form you declare that you will not use www.vagabond.bg for the purpose of violating the laws of the Republic of Bulgaria. When commenting on www.vagabond.bg please observe some simple rules. You must avoid sexually explicit language and racist, vulgar, religiously intolerant or obscene comments aiming to insult Vagabond Media Ltd, other companies, countries, nationalities, confessions or authors of postings and/or other comments. Do not post spam. Write in English. Unsolicited commercial messages, obscene postings and personal attacks will be removed without notice. The comments will be moderated and may take some time to appear on www.vagabond.bg.


Add new comment